
NovaGuard › Product Documentation › NovaGuard 6.04R4 User Manual › 4.7.3.1 Traffic Forwarding
4.7.3.1 Traffic Forwarding
NovaGuard uses the traffic forwarding feature to collect the original traffic from a host's NIC and forward it to the NovaCommand device for threat analysis. To enable this feature, you must integrate NovaGuard with NovaCommand.
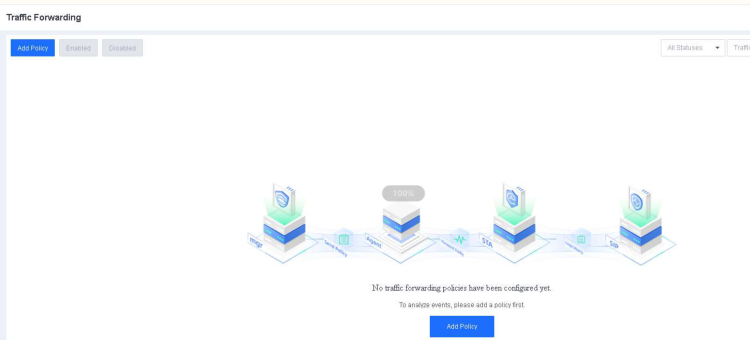
To configure a forwarding policy, click Add Policy and set the following parameters.
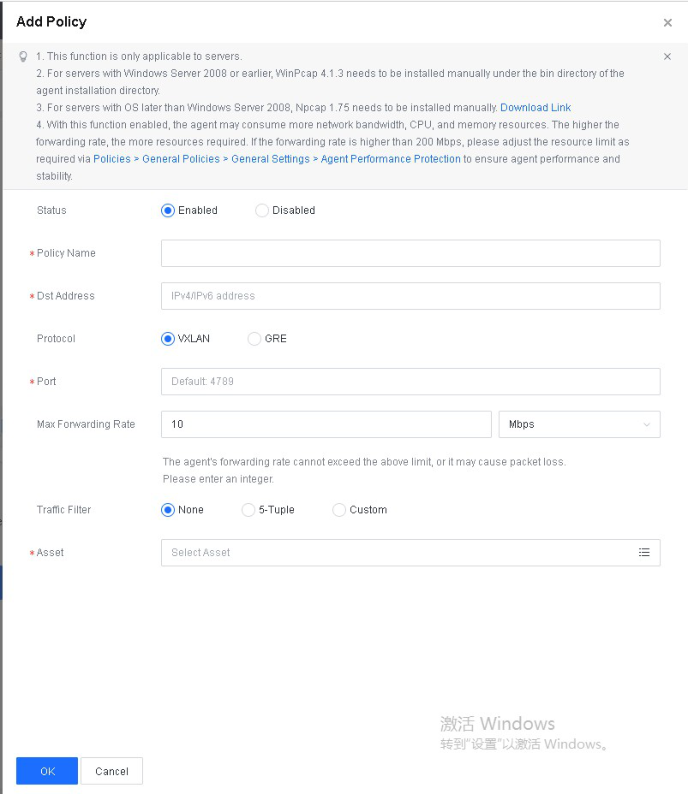
Specify the IP address of the STA device for Dst Address ; select VXLAN or GRE for Protocol ; set the value of Max Forwarding Rate below 1 Gbit/s; and specify a value for Traffic Filter, where None indicates that the traffic is
collected without filtering and 5-Tuple indicates that the 5-tuple attributes are collected.

NovaGuard 6.04R4 Manual.pdfPDF · English · 24.1 MB
Download